Firewalls
Protect devices from unauthorised connections and ensure firewall rules are appropriately configured.
CYBER ESSENTIALS. MADE SIMPLE
SecureX7 assesses your environment against Cyber Essentials, identifies the gaps, creates a step-by-step plan and guides you through the remediation needed to get certification ready and stay that way.
 Automated Assessment
 Prioritized remediation
 Evidence made easy
Built to align with Cyber Essentials v3.3 technical requirements
Preparing for Cyber Essentials certification often requires significant manual effort, collecting evidence, checking device configurations and validating security controls. And not least, trying to read and understand the requirements for infrastructure and the associated questionnaire.
SecureX7 automates this process by continuously assessing your endpoints against Cyber Essentials technical requirements, identifying non-compliant devices, weak security, and configuration settings that leave you open to attack, providing prioritised remediation guidance before they become Certification Blockers.
And because SecureX7 is an AI-native technology, it will also fast-track you through the non-technical aspects of the compliance process too, simplifying the workload and saving time. It’s like having your own Private Cyber Essentials Consultant whenever you need!
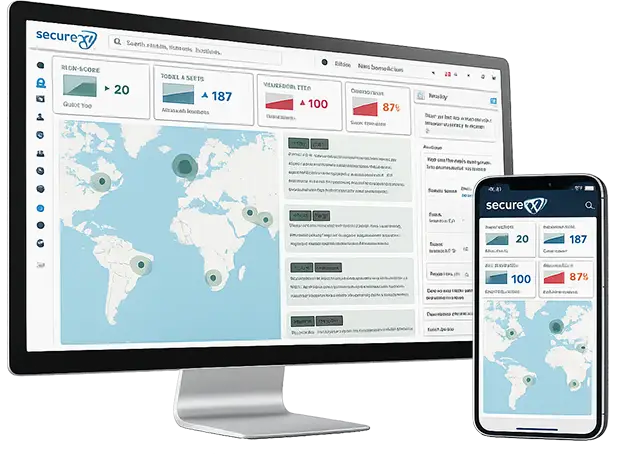
Cyber Essentials keeps your business safe by implementing fundamental security controls consistently across every device, which means that continuous monitoring is far more effective than performing periodic manual audits. SecureX7 continually validates endpoint configurations, allowing organisations to maintain compliance throughout the year rather than rushing to prepare for annual certification. It will also provide executive dashboards, compliance scoring and detailed reporting that can be shared with internal stakeholders or external assessors, significantly reducing the administrative burden associated with evidence collection.
Instead of treating a self-led certification as a one-off examination, SX7 gets you on course to maintain Cyber Essentials readiness every minute of every day, which means your business is cyber-secure, 24/7.
Not everyone is a security expert, and even cyber security professionals still have limited time to research and plan Vulnerability remediation plans.
Being built on embedded AI expertise, SecureX7 will do the heavy lifting for you, not just analysing your exposed attack surface and identifying weak spots, but guiding you through technical remediation procedures, optimised for your experience and resources
Typical benefits include:
CYBER ESSENTIALS MADE SIMPLE
SecureX7 automatically assesses your environment, identifies potential Cyber Essentials gaps, creates a prioritized workplan and guides you through remediation, so you can achieve Cyber Essentials with confidence.
“I need to get Cyber Essentials compliant.”
Simply tell SecureX7 your goal and it will guide you through the process.
Stop guessing. See what needs attention.
SecureX7 assesses your environment against the relevant Cyber Essentials requirements and helps identify the controls, devices and configurations that require attention.
From findings to a prioritized Workplan.
SecureX7 turns identified issues into a practical, prioritized remediation Workplan showing your team what needs fixing and in what order.
Practical guidance through the remediation journey.
“What do I need to do to fix this?”
Know when the job is actually done.
Once remediation work has been completed, SecureX7 helps you reassess the environment and verify that identified issues have been addressed.
PRODUCT DEMONSTRATION
Watch our six-minute introduction and demonstration of SecureX7 and see how it helps you understand your environment, assess your security posture, prioritize risks and take action.
Cyber Essentials certification demonstrates that your organisation has five fundamental technical controls in place to protect against the most common cyber threats.
The certification process is straightforward, but good preparation can make the difference between a smooth assessment and discovering problems after you have started.
1. Define your scope
Identify the devices, networks, cloud services and users covered by your assessment.
2. Assess your environment
Check your systems against the five Cyber Essentials controls and identify configuration, software, vulnerability and access-control gaps.
3. Remediate weaknesses
Fix the issues you discover and confirm that your devices meet the required security baseline.
4. Complete the assessment
Submit the Cyber Essentials self-assessment questionnaire to an authorised Certification Body for review by a qualified assessor.
5. Maintain compliance
Certification lasts 12 months, but your IT environment changes continuously. New devices, software, vulnerabilities and configuration changes can introduce new risks before your next assessment.
SecureX7 helps you assess, remediate and continuously monitor your Cyber Essentials readiness — so you can approach certification with confidence.
Cyber Essentials focuses on five technical controls designed to protect your organisation against the most common cyber attacks. They sound straightforward, but each requires you to understand how your devices and systems are actually configured.
Protect devices from unauthorised connections and ensure firewall rules are appropriately configured.

Remove unnecessary accounts, applications and services, change insecure defaults and configure devices securely.

Keep operating systems, applications and firmware supported and apply important security fixes within the required timescales.

Give users only the access they need, control administrative privileges and use appropriate authentication and MFA.

Protect devices against malicious software using appropriate technologies such as anti-malware protection, application allowlisting or application sandboxing.
SecureX7 helps you assess the technical conditions behind these controls, identify weaknesses and prioritise the changes required to improve Cyber Essentials readiness.
Before assessing your Cyber Essentials readiness, you need to establish exactly what is being assessed.
Your scope can include desktop and laptop computers, servers, mobile devices, network equipment and cloud services. Remote workers and personally owned devices may also need to be considered depending on how they access organisational data and services.
Getting this wrong can create problems later. An overlooked laptop, unsupported application, cloud service or internet-facing system could materially change your answers to the Cyber Essentials assessment.
The objective is therefore to establish an accurate picture of your environment before completing the questionnaire: what assets do you have, where are they, what software are they running and which are included within the certification boundary?
SecureX7 provides asset discovery and inventory capabilities that can help organisations identify their technology estate and uncover systems that might otherwise be missed.
Cyber Essentials and Cyber Essentials Plus are based on the same five technical controls. The important difference is how those controls are verified.
Cyber Essentials is based on a self-assessment questionnaire. Your organisation confirms how its systems are configured and a qualified assessor reviews the answers before certification is awarded.
Cyber Essentials Plus goes further. It adds independent technical verification to test whether the controls described in your assessment are operating effectively across a representative sample of your environment.
For many organisations, Cyber Essentials provides an appropriate starting point. Others choose Cyber Essentials Plus because customers, contracts or internal security requirements demand a higher level of independent assurance.
Whichever certification you pursue, the underlying challenge is the same: understanding your environment, finding weaknesses and correcting them before assessment.
SecureX7 helps organisations establish this technical readiness before entering the certification process.
The cost of Cyber Essentials certification depends primarily on the size of your organisation, while Cyber Essentials Plus costs more because it includes independent technical testing.
But the certification fee is only part of the real cost.
Organisations may also need to spend time identifying assets, reviewing security settings, updating software, removing unsupported applications, correcting configuration weaknesses and gathering the information required to complete the assessment accurately.
The timescale therefore depends heavily on how prepared your environment already is. An organisation with an accurate inventory and well-managed security baseline may progress quickly; one that discovers unsupported software, excessive administrative privileges or inconsistent configurations may require remediation first.
This is why assessing your environment before starting certification can be valuable.
SecureX7 helps identify potential compliance gaps and prioritise remediation, giving you a clearer picture of the work required before submitting your assessment.
Cyber Essentials is a self-assessment, but that doesn't mean the best approach is simply to start answering the questionnaire.
Good preparation begins by understanding your scope and establishing an accurate inventory of the devices, software and services being assessed. You can then check your environment against each of the five technical controls and address weaknesses before submitting your answers.
Typical issues include unsupported software, missing security updates, unnecessary administrator accounts, insecure configurations and inconsistent endpoint protection.
You should also retain information that supports the answers you provide. Asset inventories, software versions, security configurations and remediation records can all help create a clearer picture of your compliance position.
SecureX7 helps automate much of this technical preparation by discovering assets, assessing security posture, identifying potential compliance gaps and tracking remediation.
The result is a more evidence-led approach to Cyber Essentials rather than relying entirely on manual checks and assumptions.
Passing Cyber Essentials confirms your compliance at assessment, but your IT environment doesn't stand still.
A new laptop is deployed. Someone installs an application. A security setting changes. A vulnerability is discovered. Software reaches end of support. An administrator account is created.
Individually these may appear routine. Collectively they can move an organisation away from the security baseline it established during certification.
This is the difference between passing Cyber Essentials once and maintaining Cyber Essentials readiness continuously.
SecureX7 continually helps organisations understand their technology estate, identify configuration weaknesses and vulnerabilities, prioritise remediation and monitor changes that could affect their security posture.
Instead of rediscovering your compliance position when certification comes up for renewal, you maintain visibility throughout the year.
Cyber Essentials
Our role is to make it much more straightforward to understand, implement and operate Cyber Essentials best practices for your organisation.
SecureX7 does this by automatically assessing endpoint configurations, identifying potential certification blockers, prioritising remediation and supporting evidence collection so that your self-certification or auditor scrutiny is much easier.
Yes, cloud services used by the organisation may fall within the assessment scope. Responsibility is shared between your organisation and the cloud provider, so settings such as user access, administrative privileges and multi-factor authentication still need to be considered.
SecureX7 continuously assesses supported endpoints against relevant Cyber Essentials technical requirements. It identifies non-compliant devices and insecure configurations, explains why they matter and provides prioritised guidance to help correct them.
Remember: this isn’t just about getting through the audit. It’s about making sure your business is as cyber-safe as it can be at all times.
No. Some requirements can be validated technically, while others depend on organisational scope, policies, processes or information supplied by your business.
SecureX7 automates applicable technical checks and provides AI-assisted guidance for requirements that need human input.
Yes. The same five controls apply to Cyber Essentials Plus, but their implementation is independently tested. SecureX7 can help identify weaknesses and address potential failures before technical testing begins.
The final assessment and testing must still be completed by an authorised Certification Body.
The time required depends on the size and complexity of your environment, the accuracy of your asset inventory and the number of issues requiring remediation.
SecureX7 helps reduce preparation time by automating applicable checks and showing which problems should be addressed first.
SecureX7 provides compliance scoring, device-level findings, remediation status and reports that can support internal reviews and certification preparation.
Your assessor may also request additional evidence or clarification depending on your environment and chosen certification level.
Begin by identifying the devices, software and cloud services within your proposed certification scope.
SecureX7 can then assess supported endpoints, highlight potential compliance gaps and provide a prioritised plan for improving readiness.
GET STARTED TODAY
Join us at SecureX7, in redefining the future of cybersecurity.